AI Agents at Work: Microsoft Tightens Controls as Only 26% of Enterprises Are Ready
Within a few days in mid-October 2026, two major signals pointed in the same direction: AI agents have moved into real business operations, but the ability to govern them is still catching up.
Microsoft: treat AI agents like insiders
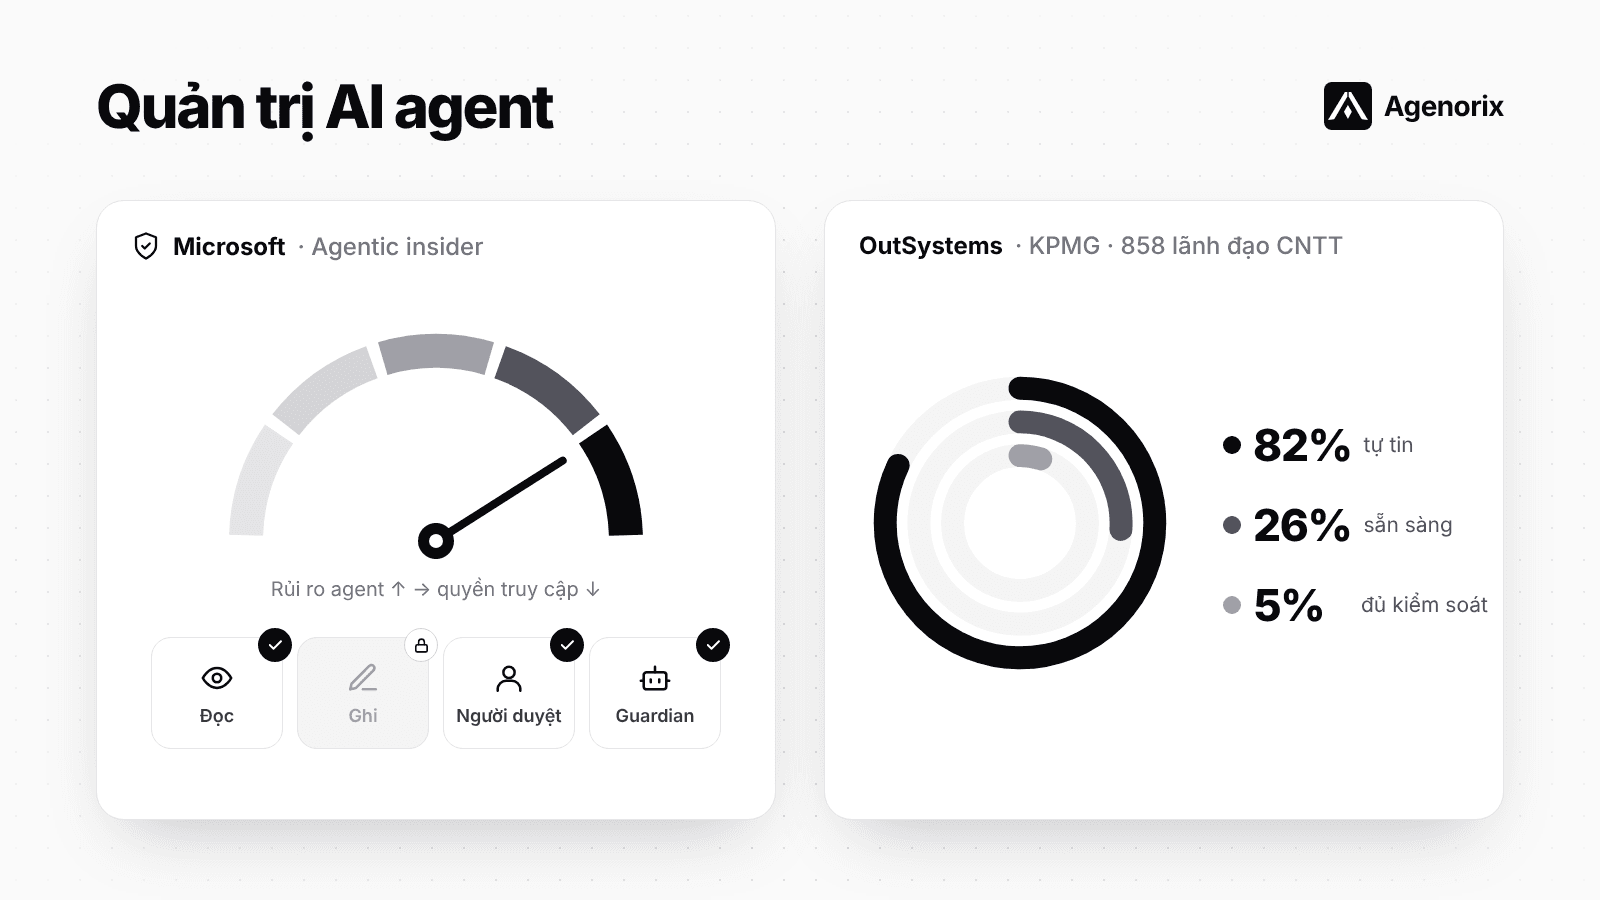
On October 19, 2026, Microsoft announced new controls for the "agentic insider" risk: the risk posed by AI agents operating inside an organization. The reasoning: agents are often granted more permissions than they need, so they should be monitored like employees with privileged access.
Dynamic risk scores: every agent gets a continuously updated risk score built from identity, data, network and its own activity.
Risk-adaptive access: the higher the risk, the narrower the permissions, from losing write access, to requiring human approval, to being isolated or stopped.
Guardian Agents: supervising agents watch other agents, while people still set the rules and keep control of important decisions.
Some capabilities remain in limited preview.
OutSystems: only 26% of enterprises are ready to handle agent conflicts
On October 16, 2026, OutSystems released Engineering Business Outcomes: The Shift to Agentic Systems, produced with CIO Dive and KPMG and based on a survey of 858 technology leaders:
82% say their organizations can keep pace with governing and monitoring agents.
Yet only 26% are well prepared to resolve conflicts between agents, systems and automated workflows.
And just 5% have automated controls, audit trails and human review points fully in place.
As vendor-sponsored research, these figures are best read as a directional signal.
The Agenorix view: design governance in from day one
When we deploy AI agents for businesses, the question is no longer "should we use them?" but "what is this agent allowed to do, who is accountable, and how do we verify it?" That is why every agent we take to production follows five principles from the very first release:
Agent inventory: every agent has an owner and a clear scope.
Least privilege (RBAC): only the permissions the task needs, time-bound.
Human checkpoints: for every irreversible action.
Full audit logging: every action is traceable.
Continuous monitoring: with clear rules for when agents conflict.
Where should businesses start?
For each agent you run, ask three questions: what permissions does it hold, who approves its important actions, and where are its activity logs? Any agent that cannot answer all three is where to focus first. If you want to review your agents or bring AI agents into your workflows, the Agenorix team is ready to help, and your first consultation is free: get in touch.
Sources: Microsoft Security Blog (Oct 19, 2026), TechCrunch, SiliconANGLE; OutSystems release via PR Newswire (Oct 16, 2026), FutureCIO.
Share